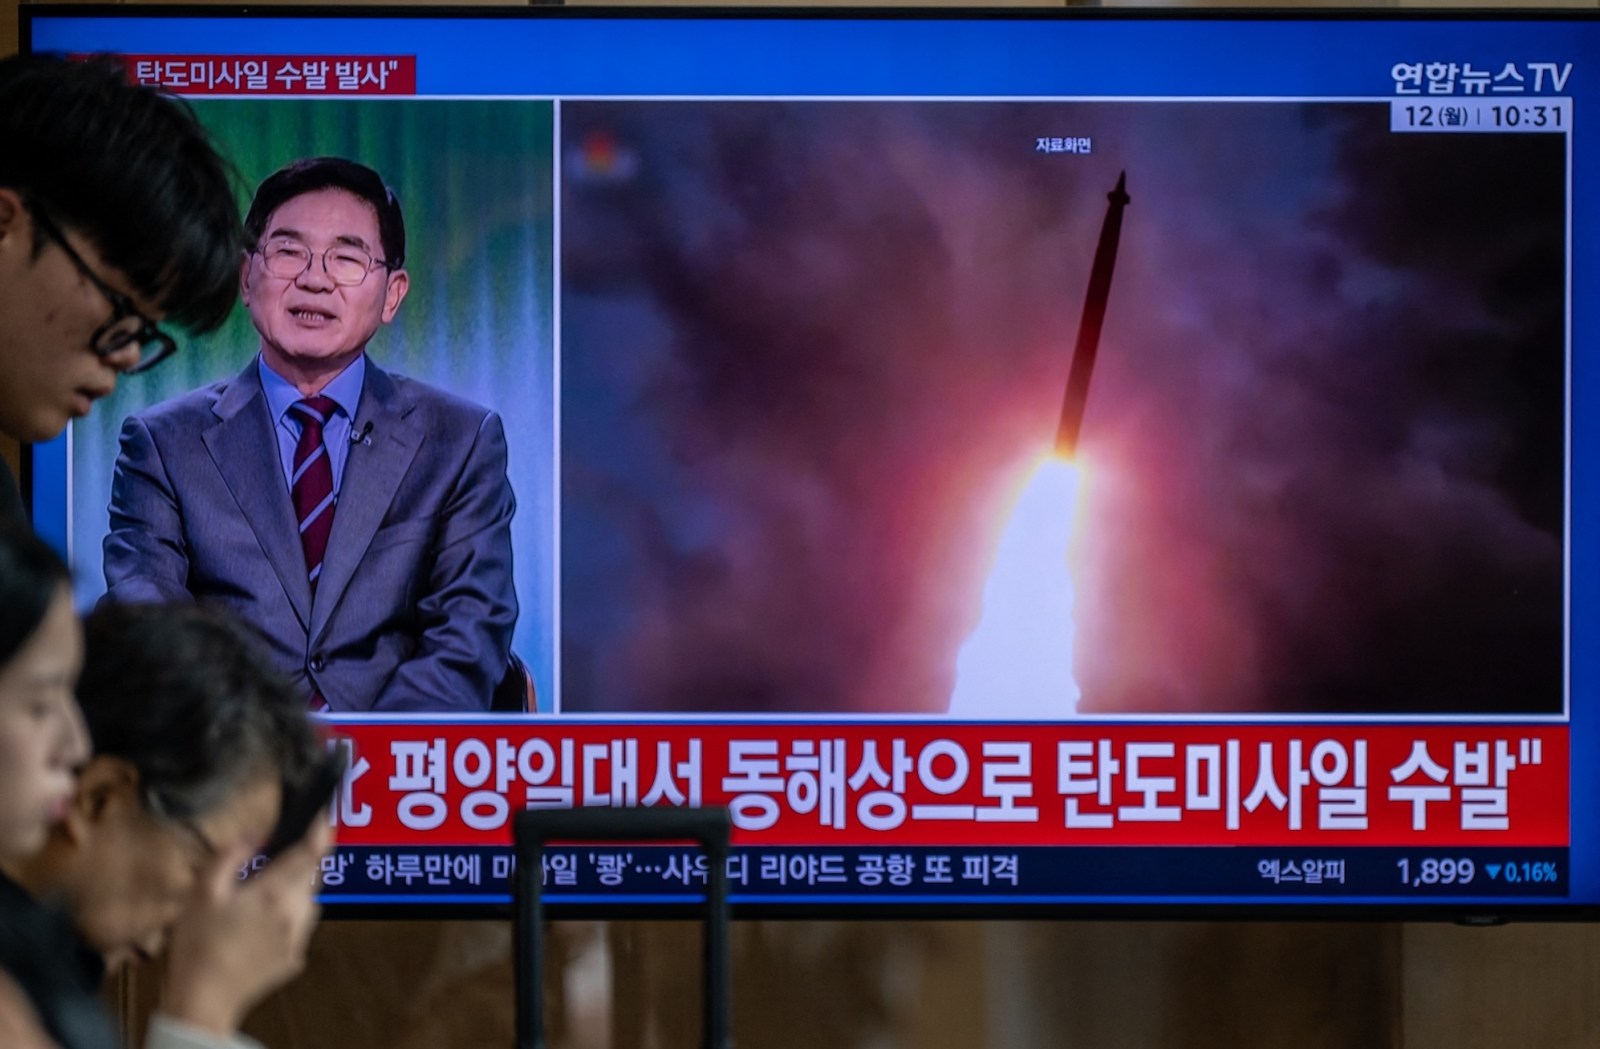
The U.S. Department of Justice is alerting that cyber operatives employed by the North Korean government are progressively enlisting Americans to assist in breaching American businesses.
During a Tuesday announcement, prosecutors disclosed they have charged and apprehended a minimum of two individuals, and executed searches at numerous suspected “laptop farms” throughout Texas. These devices were purportedly utilized by North Koreans to remotely infiltrate U.S. firms and exfiltrate confidential information.
Per the DOJ, federal agents confiscated more than 180 computers that U.S. businesses had dispatched to recent hires, unaware these recruits were sanctioned North Korean operatives who had assumed stolen American identities to secure positions.
The department stated it raided upwards of 40 laptop farms across Texas — the greatest publicly revealed count of dwellings employed to enable North Korean cyber intrusions — operated by a minimum of two American intermediaries.
CrowdStrike, which assisted the FBI in probing and disrupting the most recent North Korean campaigns, stated that laptop farms are “essential” for North Korea in enabling its hackers to surmount the physical, monetary, and legal obstacles of not being physically present in the United States.
Prosecutors indicated that a minimum of 70 U.S.-based enterprises had been compromised by the intruders, who are estimated to have amassed approximately $3 million in pilfered proceeds. The DOJ declined to identify the victimized firms but characterized them as spanning healthcare, cyber support, retail, communications, and manufacturing sectors across Ohio and 16 additional states, plus the District of Columbia.
“Increasingly, North Korean IT personnel are resorting to enlisting American intermediaries to circumvent enhanced private-sector detection and law enforcement measures. These operatives are engaging facilitators for a broader range of duties, and in certain instances outsourcing entire assignments to third-party foreign nationals,” the Justice Department stated.
Frequently, North Korean cyber actors employ authentic-appearing email addresses, fabricated LinkedIn profiles, and elaborate online and social media presences as camouflage for their operations.
In a separate public service announcement, the FBI declared that “thousands” of North Korean state-directed IT workers are embedded at Western firms, which “present a substantial national security and intellectual property theft insider threat.”
This marks the most recent surge of arrests, indictments, and enforcement actions aimed at North Korean operations within the United States in recent years. The isolated regime has leveraged this “remote IT workers” scheme to enable North Koreans to secure employment with U.S. and European companies, collect salaries, and subsequently pilfer sensitive data and intellectual property while on the payroll.
The targeted firms are subsequently coerced into paying the hackers additional sums.
The remote IT workers’ scheme constitutes one of multiple illicit revenue streams the North Korean regime seeks to cultivate, alongside compromising cryptocurrency exchanges and open-source developer initiatives, all intended to finance its internationally sanctioned nuclear weapons program. The regime is believed to have absconded with at least $2 billion in cryptocurrency during 2025 alone.
North Korea specialists assess that the count of compromised companies and the volume of stolen cryptocurrency are likely substantially greater than disclosed.
Earlier this year, CrowdStrike reported in a separate analysis that North Korean hackers were responsible for approximately half of all documented “hands-on-keyboard” intrusions over the prior year, denoting breaches executed by human operators rather than automated tools or AI.